Threat intel, DFIR
and security notes
Deep-dives, investigation write-ups, tooling notes and transparent product updates from the mlab team. Written for analysts who want the indicators, the method and the fix.
#supply-chain
Newest first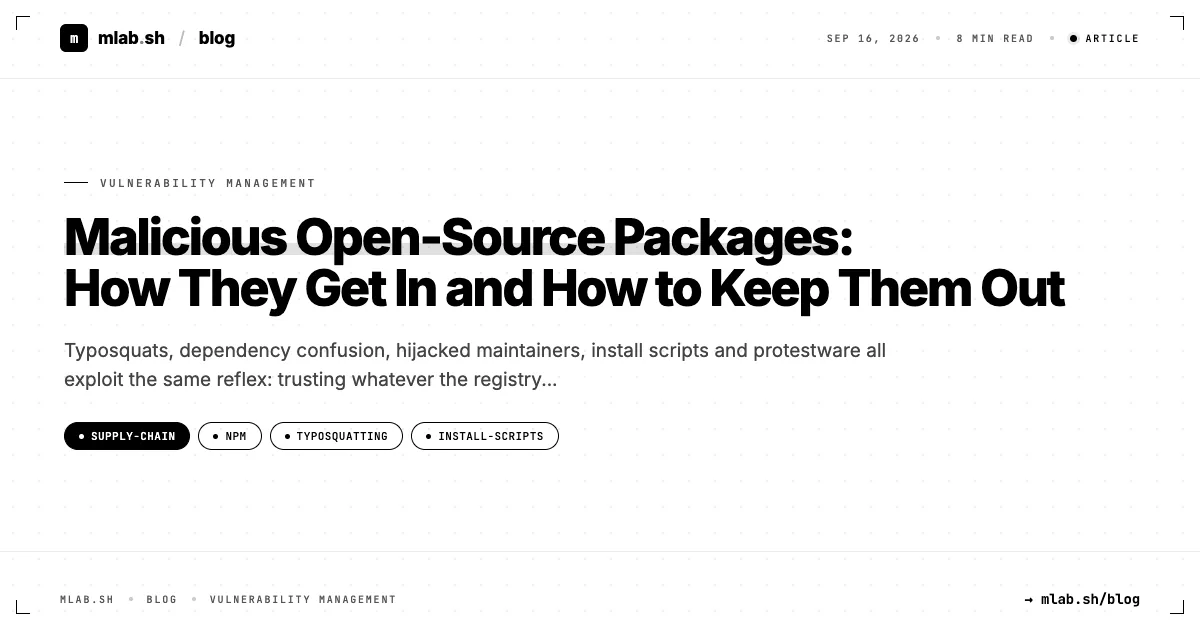
Malicious Open-Source Packages: How They Get In and How to Keep Them Out
Typosquats, dependency confusion, hijacked maintainers, install scripts and protestware all exploit the same reflex: trusting whatever the registry hands you. How each technique works, how to vet a dependency in ten minutes, and why a release cooldown is the cheapest control you are not using.
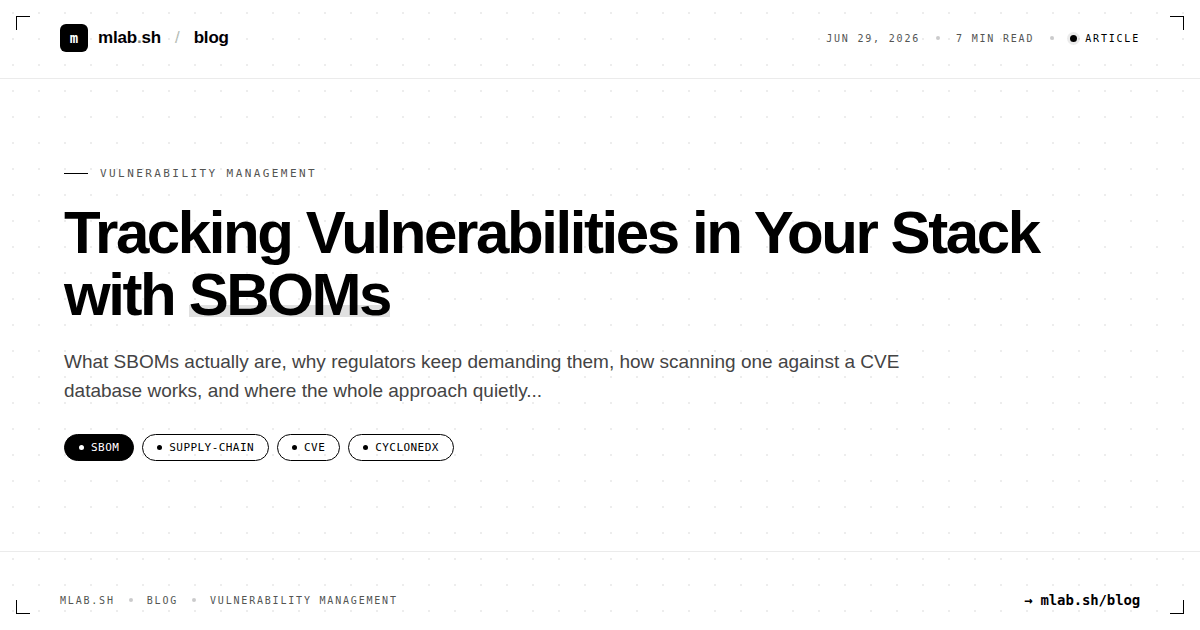
Tracking Vulnerabilities in Your Stack with SBOMs
What SBOMs actually are, why regulators keep demanding them, how scanning one against a CVE database works, and where the whole approach quietly breaks.
Third-Party Risk Management Without the Spreadsheet Nightmare
Vendor questionnaires are point-in-time, self-reported, and unread. Here is why the spreadsheet model of TPRM fails, what continuous vendor risk management looks like, and how DORA forces the issue.
inkdex: an index that states facts, a scanner that judges them
Studies, benchmarks and build notes. Method first, numbers included, losses too.
Read the latest note