Threat intel, DFIR
and security notes
Deep-dives, investigation write-ups, tooling notes and transparent product updates from the mlab team. Written for analysts who want the indicators, the method and the fix.
All articles
Page 2 of 9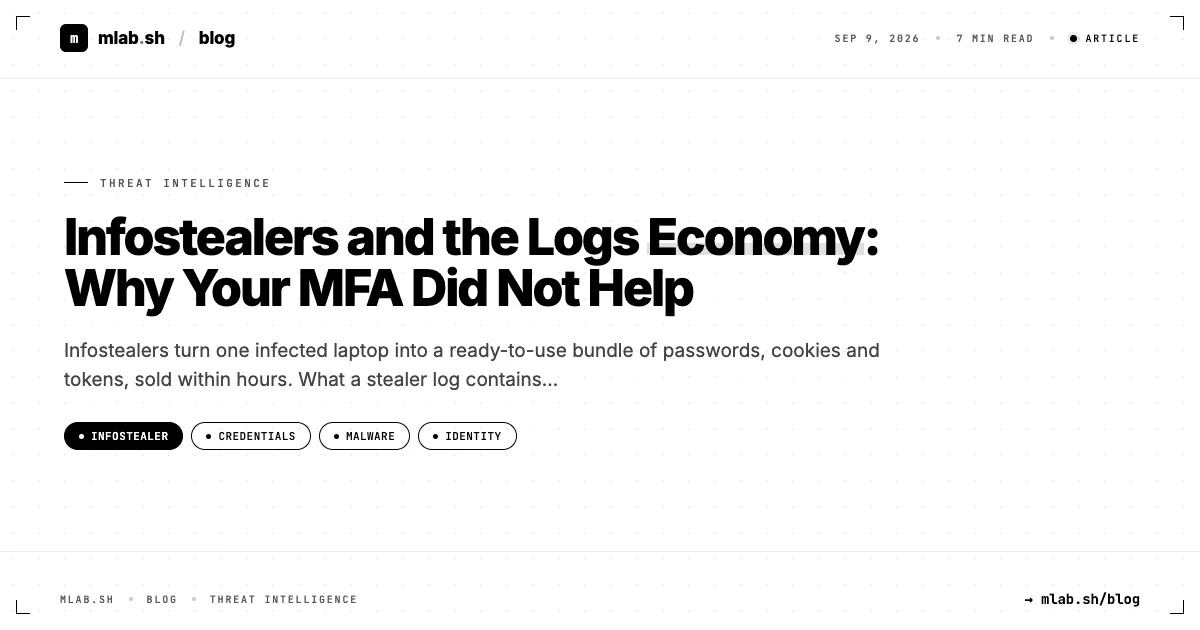
Infostealers and the Logs Economy: Why Your MFA Did Not Help
Infostealers turn one infected laptop into a ready-to-use bundle of passwords, cookies and tokens, sold within hours. What a stealer log contains, why session theft walks past MFA, and how defenders actually respond.
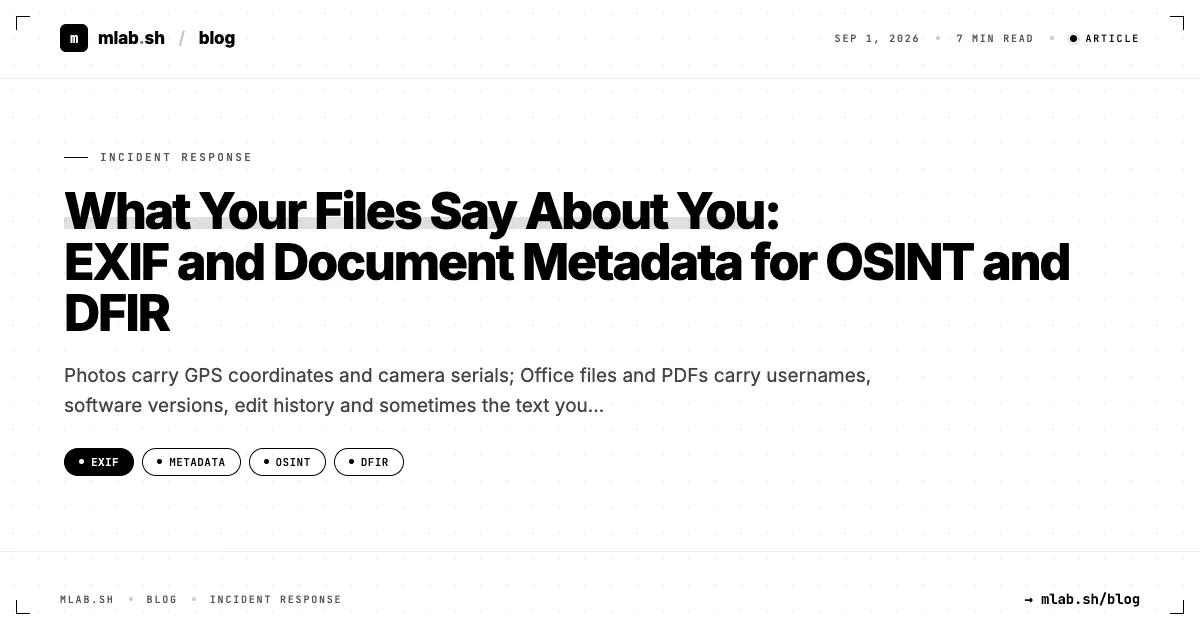
What Your Files Say About You: EXIF and Document Metadata for OSINT and DFIR
Photos carry GPS coordinates and camera serials; Office files and PDFs carry usernames, software versions, edit history and sometimes the text you thought you deleted. What leaks, how to extract it, how stripping works, and where analysts get fooled.
The Cyber Resilience Act for Software Vendors: A Field Guide
The CRA turns secure development, SBOMs and vulnerability handling into legal obligations for anything with digital elements sold in the EU. Here is what is in scope, what the essential requirements say, and why September 2026 matters before December 2027 does.
Lookalike Domains: Punycode, Homoglyphs, Typosquats and Combosquats
A Cyrillic "а" and a Latin "a" are different domains that look identical. How IDN homoglyph attacks, punycode, typosquatting and combosquatting work, how browsers decide what to show, and how to build brand monitoring that catches lookalikes without drowning in noise.
CVSS 4.0 Explained: Reading a Vector String Step by Step
CVSS 4.0 renamed, split and added metrics, dropped Scope, and introduced labels like CVSS-BT so you know which score you are looking at. A metric by metric walkthrough of a 4.0 vector, and what changed from 3.1.
Incident Case Management: From First Alert to Final Report
Most incident response failures are bookkeeping failures: lost evidence, timelines rebuilt from memory, reports nobody can defend. How to run a case from the moment an alert gets promoted to the day the report ships.
SIEM vs SOAR Explained: What Each Does and When a Small Team Needs Which
A SIEM decides what is worth looking at; a SOAR decides what happens next. Here is where the two overlap, where XDR fits, and which one a small security team should actually buy (or build) first.
Investigating Smishing Campaigns and Suspicious Phone Numbers
Parcel fees, unpaid tolls, blocked bank cards: SMS phishing is cheap, mobile first and hard to see from the SOC. How to read a sender number or ID, what carrier and VoIP data really tells you, how to unwrap the link, and where to report so the campaign actually gets disrupted.
SOC L1/L2 Revision Guide: What to Know Cold Before the Interview
The concepts every SOC analyst interview probes: ports, protocols, HTTP codes, Windows event IDs, Sysmon, regex and CIDR. A compact revision sheet plus sample questions and how strong candidates answer them.
inkdex: an index that states facts, a scanner that judges them
Studies, benchmarks and build notes. Method first, numbers included, losses too.
Read the latest note